SGCI Governance
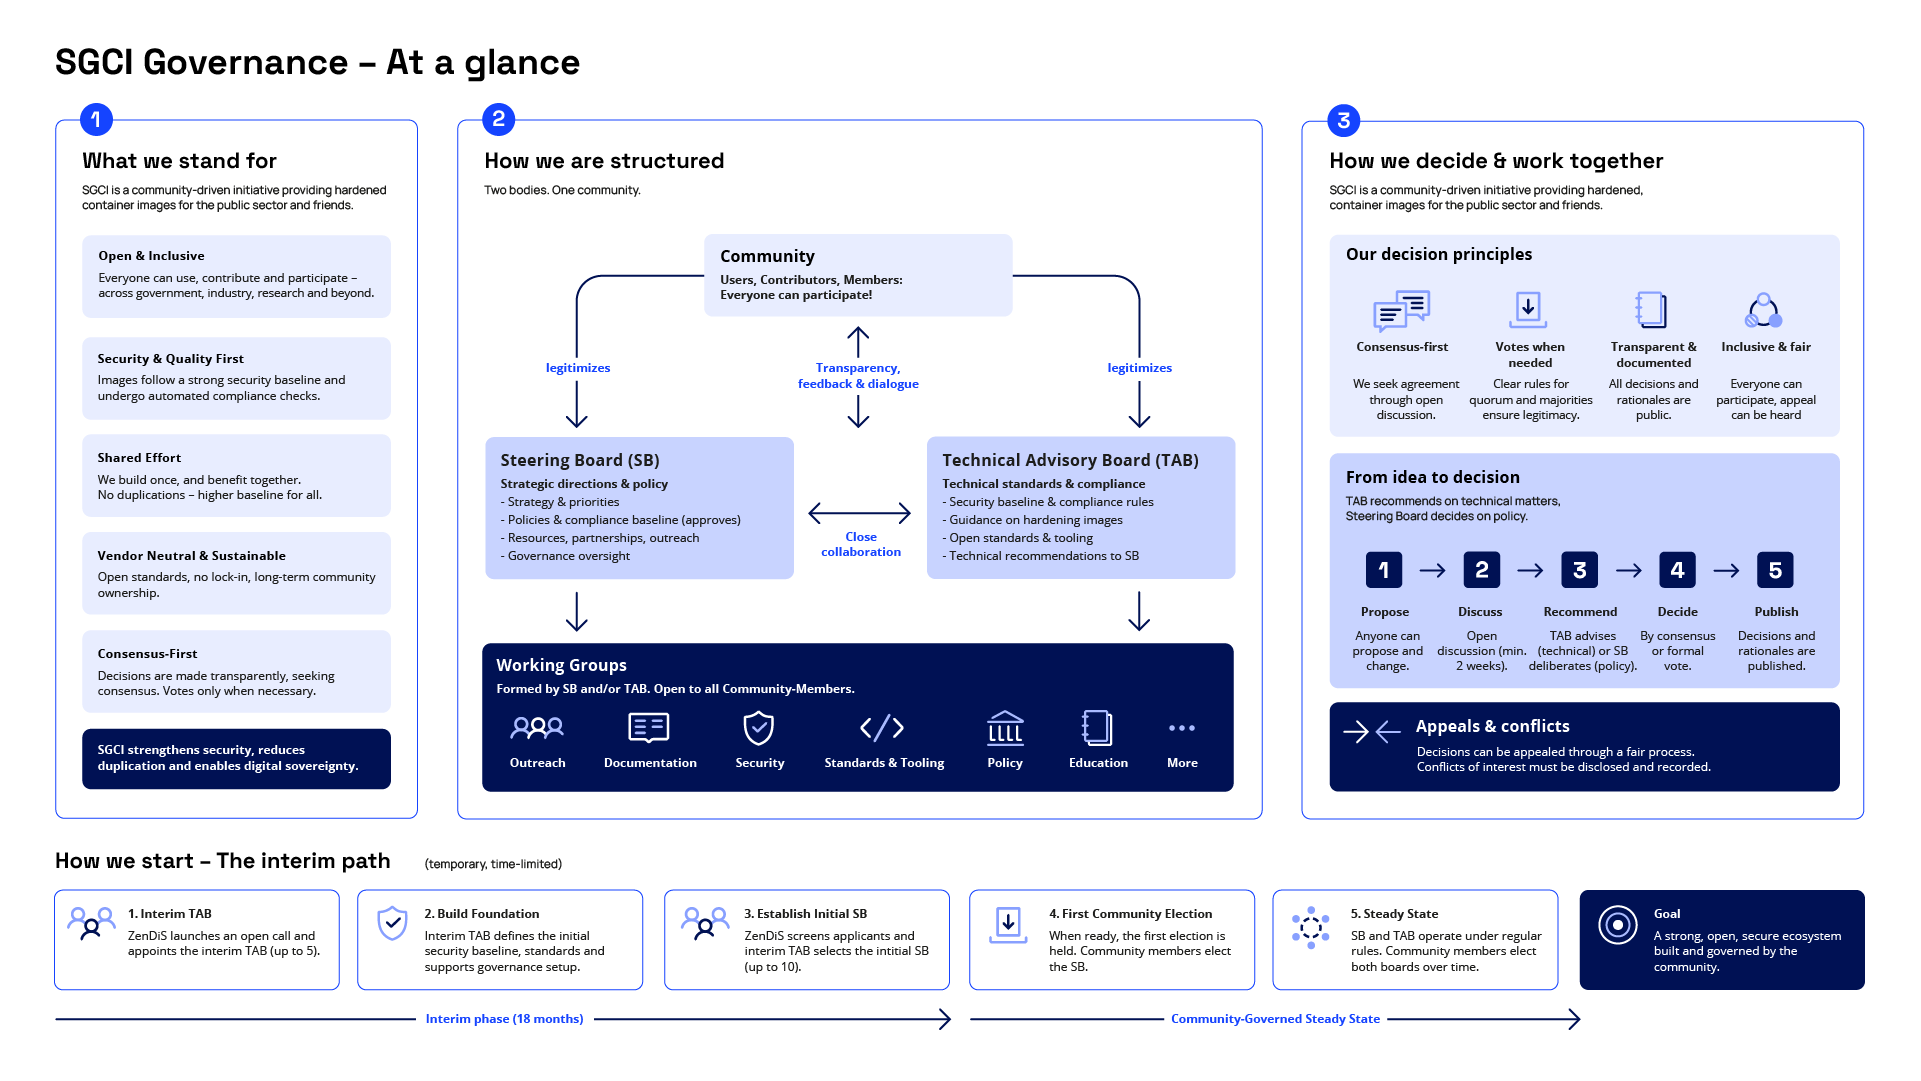
The Secure Government Container Initiative (SGCI) - the initiative behind container.gov.de - is a community-driven open source initiative within a structured governance framework tailored to public sector needs. Its governance is designed to be transparent, inclusive, and open to participation from everyone — regardless of sector or organizational affiliation.
The governance structure ensures that the initiative's technical standards, policies, and strategic direction reflect the consensus of its active community.
Mission
SGCI provides hardened container images under container.gov.de that follow security best practices and undergo automated compliance checks. Anyone can use, contribute to, and build upon them. While the initiative originated in public administration, its images and standards are open to all — government agencies, private companies, research institutions, and individuals alike.
Principles
- Openness — Everyone can participate. Discussions, decisions, and documentation are public.
- Collaboration — Shared effort over isolated work. Organizations and individuals build common building blocks together.
- Low barriers — Clear docs, accessible processes, and welcoming onboarding make it easy to contribute.
- Community ownership — Influence is earned through contribution, not affiliation. Governance serves the community.
- Automation first — Compliance checks, scanning, and quality gates are automated wherever possible for consistency and scale.
- Quality — Automated checks enforce objective baselines; human review adds judgement where automation is not sufficient.
- Consensus-first — Decisions are made by seeking consensus. Formal votes are held only when consensus cannot be reached.
- Vendor neutrality — No single organization may dominate. Governance bodies maintain balanced representation.
All community members are expected to adhere to these principles and the overall code of conduct in their participation and contributions.
Scope
SGCI focuses on providing hardened, security-compliant container images as shared building blocks. The initiative covers:
- Container image hardening — maintaining and publishing hardened base and application images on openCode and container.gov.de.
- Compliance standards — defining and enforcing rules that images must meet.
- Documentation and guidance — publishing hardening checklists, best practices, tutorials, and reference material.
- Community building — growing an active contributor base across government, industry, and research.
Motivation
Organizations across government, industry, and research rely on container technologies as a foundation for modern software deployment. Today, each organization typically hardens and reviews container images independently — duplicating effort and producing inconsistent security baselines.
SGCI addresses this by providing shared, community-maintained building blocks. Instead of every organization bearing the full cost of hardening and vulnerability assessment, images are maintained collaboratively. This approach:
- Scales security — raising the baseline for many organizations at once.
- Reduces duplication — shared effort replaces redundant, isolated work.
- Strengthens digital sovereignty — community-governed open source images reduce dependency on proprietary solutions and single vendors.
- Fosters collaboration — cross-sector participation builds trust and shared expertise.
Processes
SGCI participation spans four areas:
Use and feedback
Anyone can pull and deploy images from container.gov.de. Users test images in their environments and provide feedback by reporting issues or requesting features. User feedback is a primary input for prioritizing community work.
Image contribution and maintenance
Contributors harden new images or improve existing ones. Each image undergoes automated compliance checks and peer review before being listed. Image maintainers take ongoing responsibility for keeping their images up to date — applying security patches, resolving vulnerabilities, and responding to community feedback.
Community
The community exchanges knowledge and supports each other through public channels, open community sessions, and events. Regular meetings provide space for coordination, onboarding, and cross-organization collaboration.
Governance
Governance processes ensure fair, transparent decision-making across the initiative. This includes proposing changes to standards or policies, consensus-based decision-making within the TAB and Steering Board, and a structured appeal process.
Community
The SGCI community consists of the following roles:
User
Anyone who consumes hardened container images from container.gov.de. Users may report issues and request features but do not have voting rights in governance decisions.
Contributor
A person who actively contributes to the initiative — through code, documentation, compliance policies, image hardening, vulnerability assessments, or community support.
Member
A Contributor who has demonstrated consistent, sustained participation over time. Members may nominate candidates for governance bodies and vote in community elections. Membership criteria are defined by the Steering Board.
Governance
SGCI is governed by two bodies:
| Body | Focus | Size |
|---|---|---|
| Technical Advisory Board (TAB) | Technical standards, tooling, and compliance rules | Up to 10 members |
| Steering Board (SB) | Strategic direction, community policies, and organizational decisions | Up to 10 members |
Both bodies serve the community. Neither body operates in isolation — the TAB advises the Steering Board on technical matters, and the Steering Board sets the framework within which the TAB operates.
To understand how these bodies are initially established, see Interim Period.